Request a demo
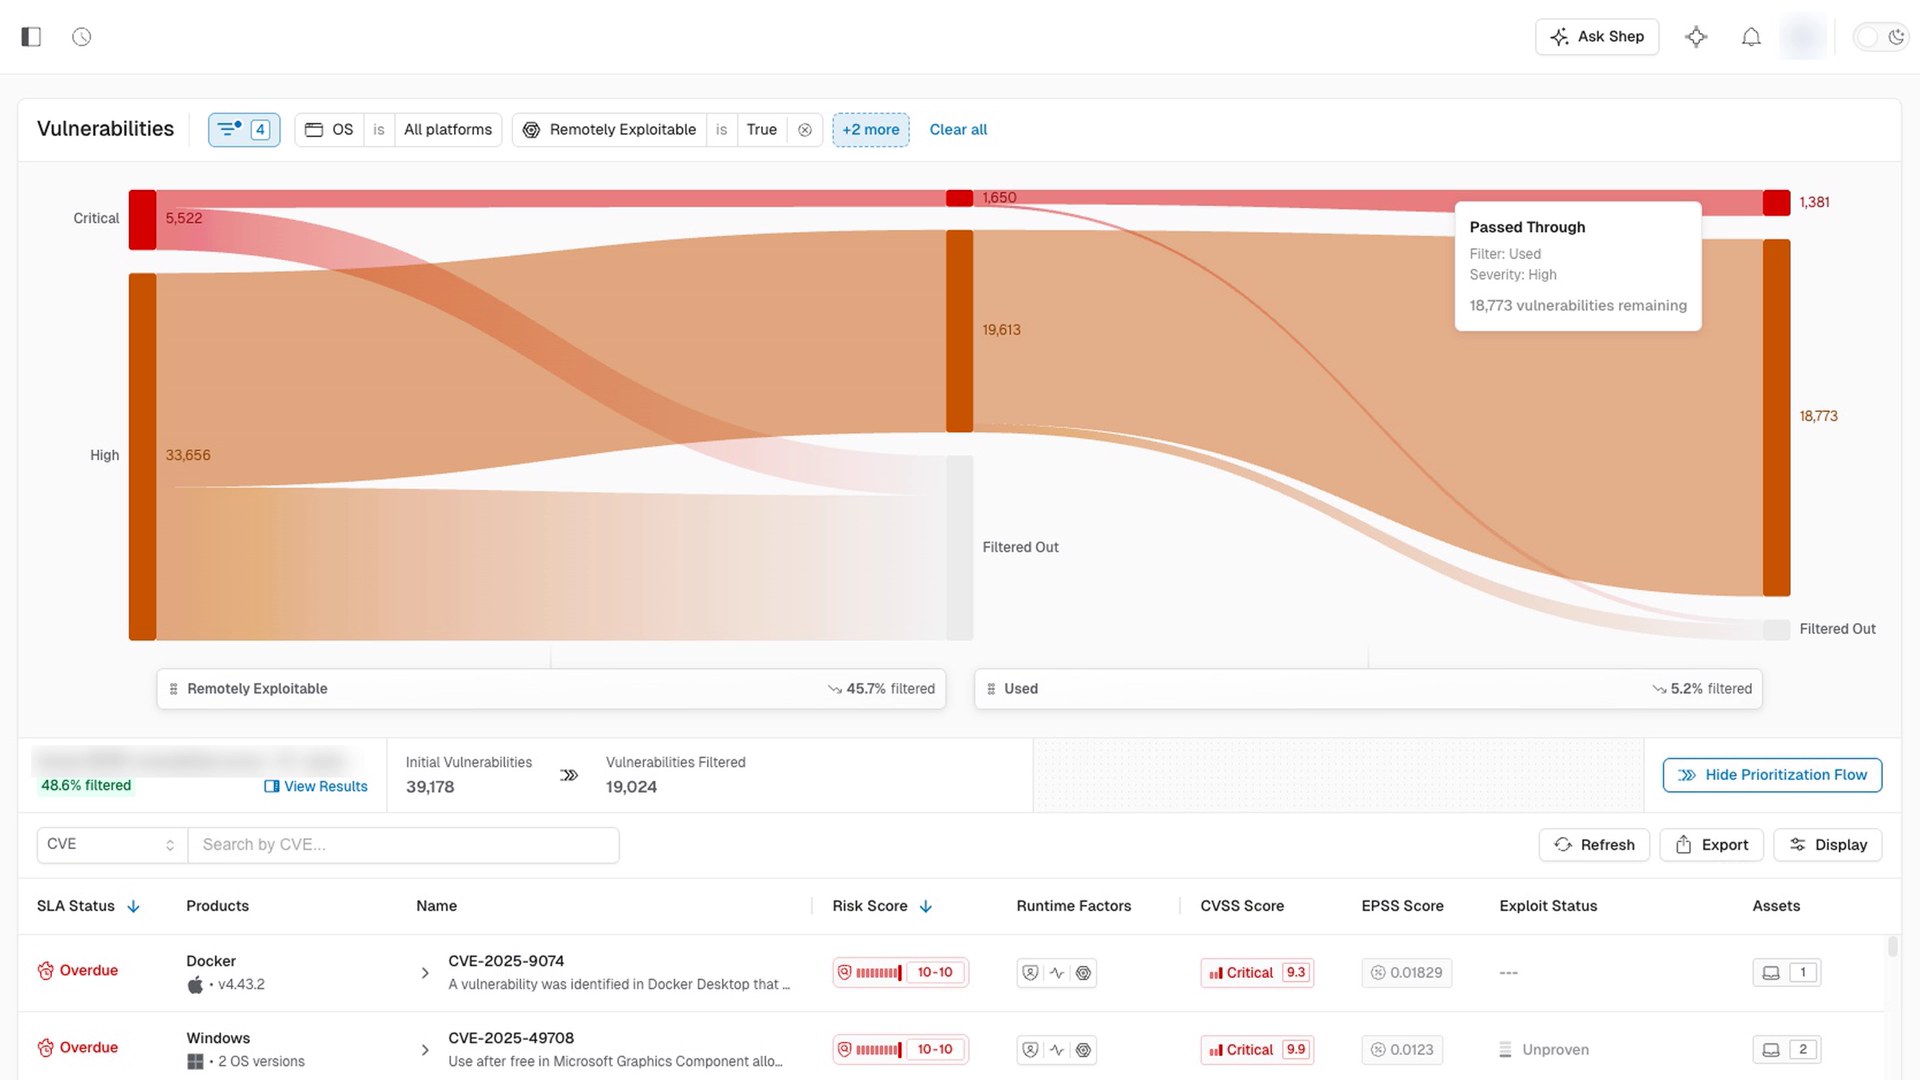
See which CVEs actually require action
Runtime evidence from one sensor shows which CVEs are exploitable on each machine, what has no CVE, and what to do when there is no patch.
01
Identify which CVEs require action
02
See what has no CVE
03
Act without a patch
Trusted by security leaders at


“We leveraged their real-time vulnerability insights to implement a risk-based approach to managing our software inventory, allowing us to focus remediation efforts where they matter most.”
Lenny Maly, CISO, Granicus
Request your demo
15 to 30 minutes, live, with Joe Silva, Spektion CEO and former Fortune 200 CISO.
Joe replies by email within one business day to set a time. The demo runs in our test environment, or on your own endpoints if you prefer. Privacy policy