See what's exploitable. Fix what matters.
Spektion shows you which CVEs are actually exploitable on each machine, finds the vulnerabilities that never get a CVE, and ships you a control when there is no patch.
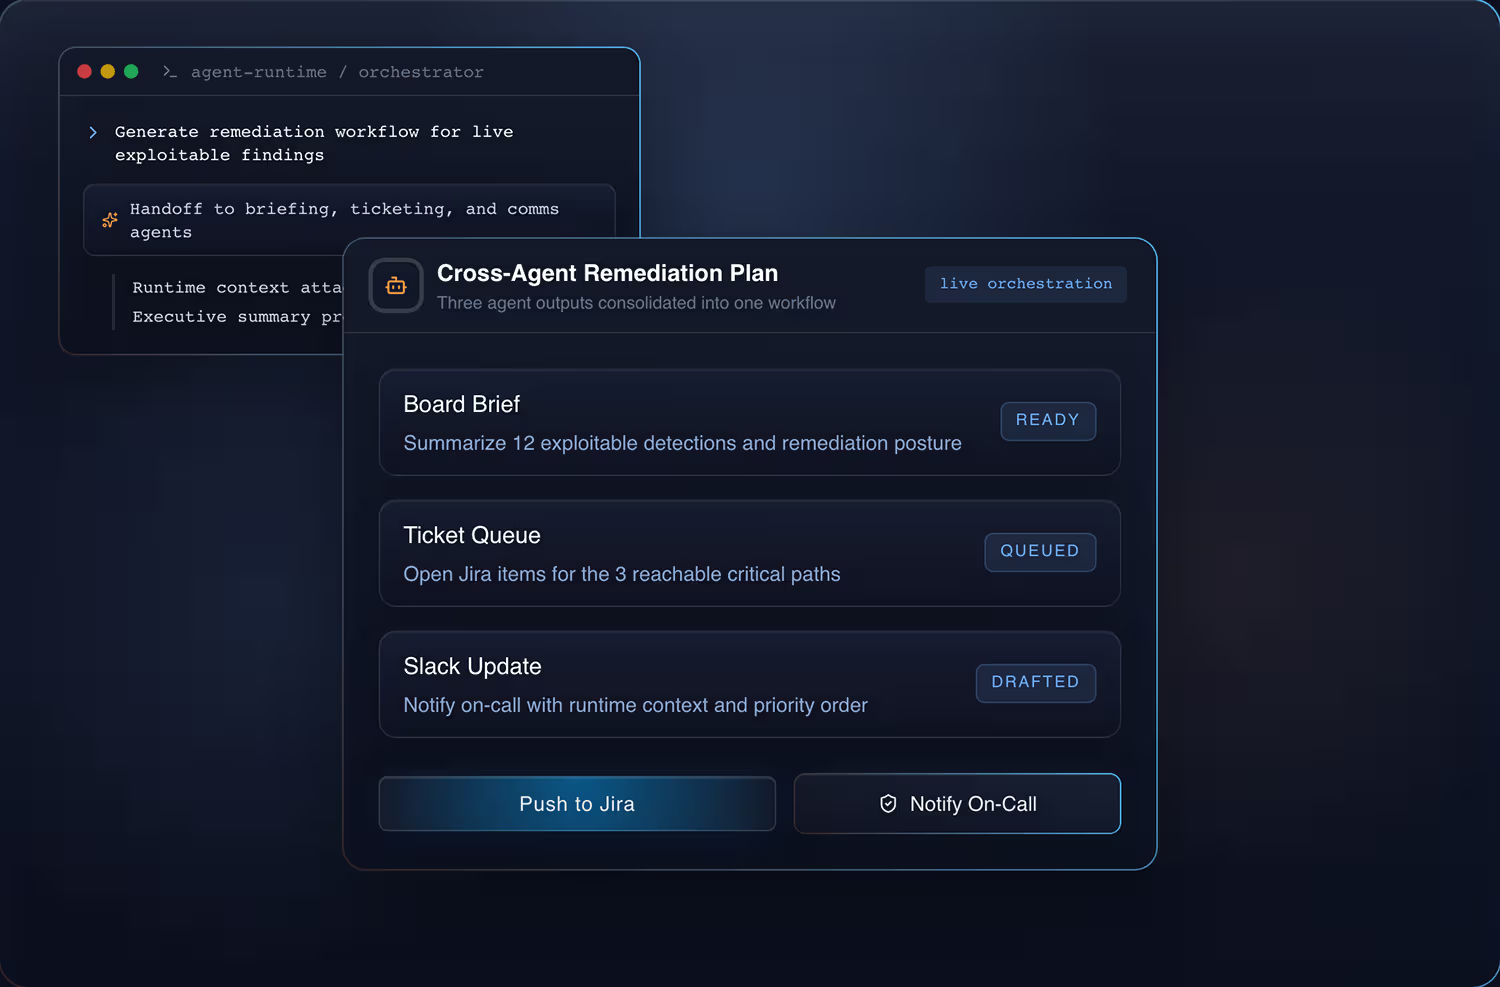
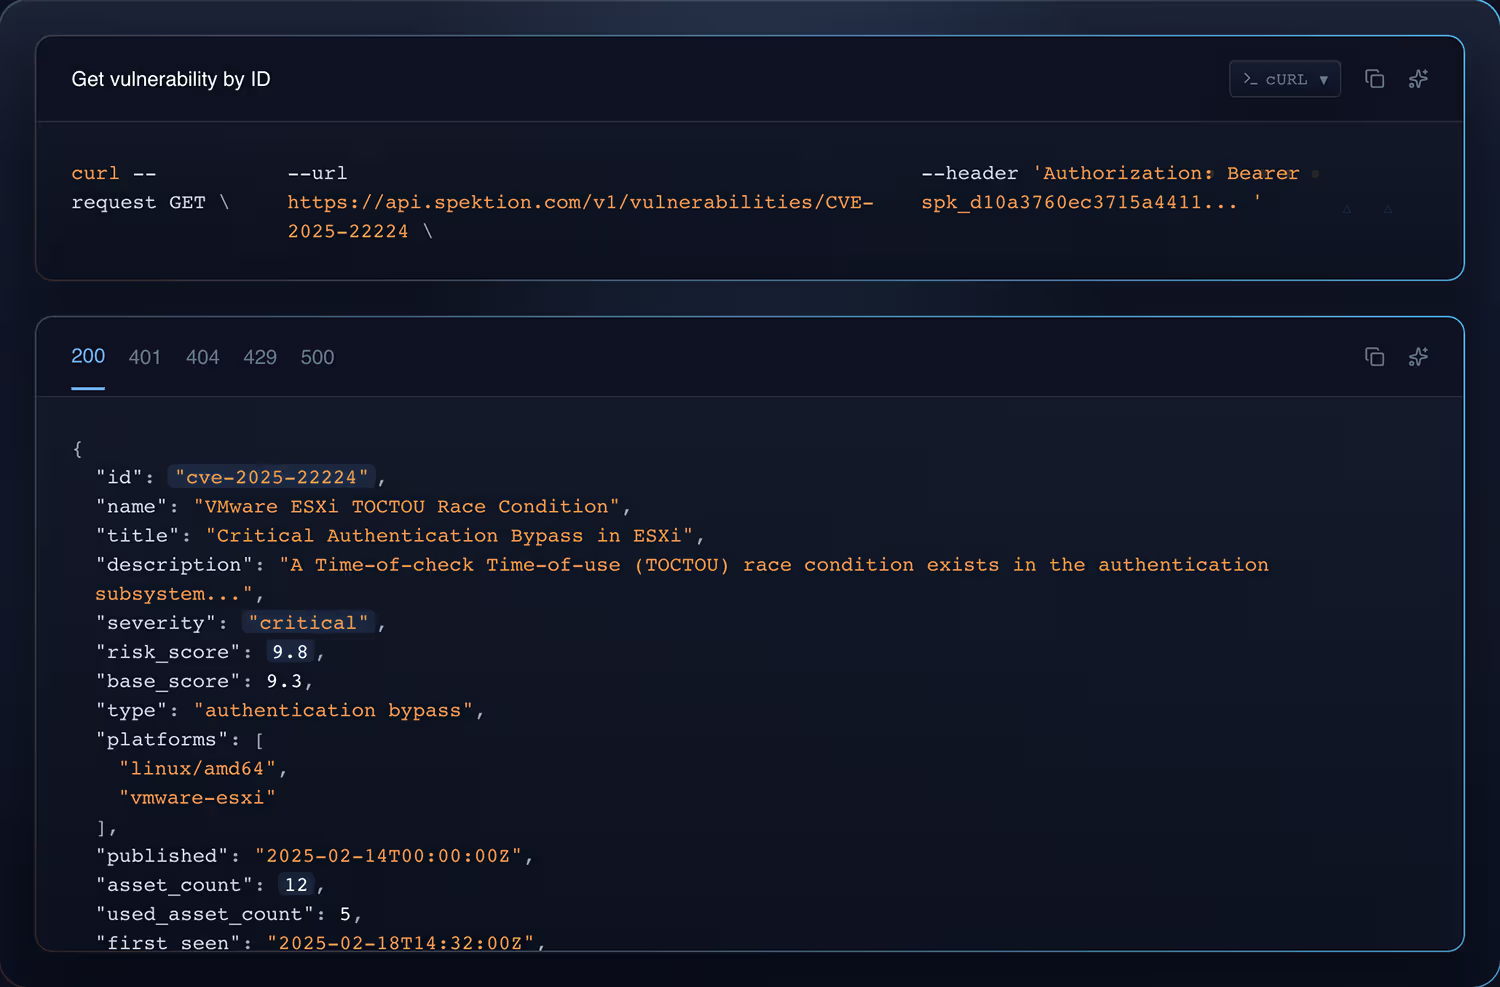


Vulnerability volume is exploding. CVEs only tell part of the story.

The volume problem
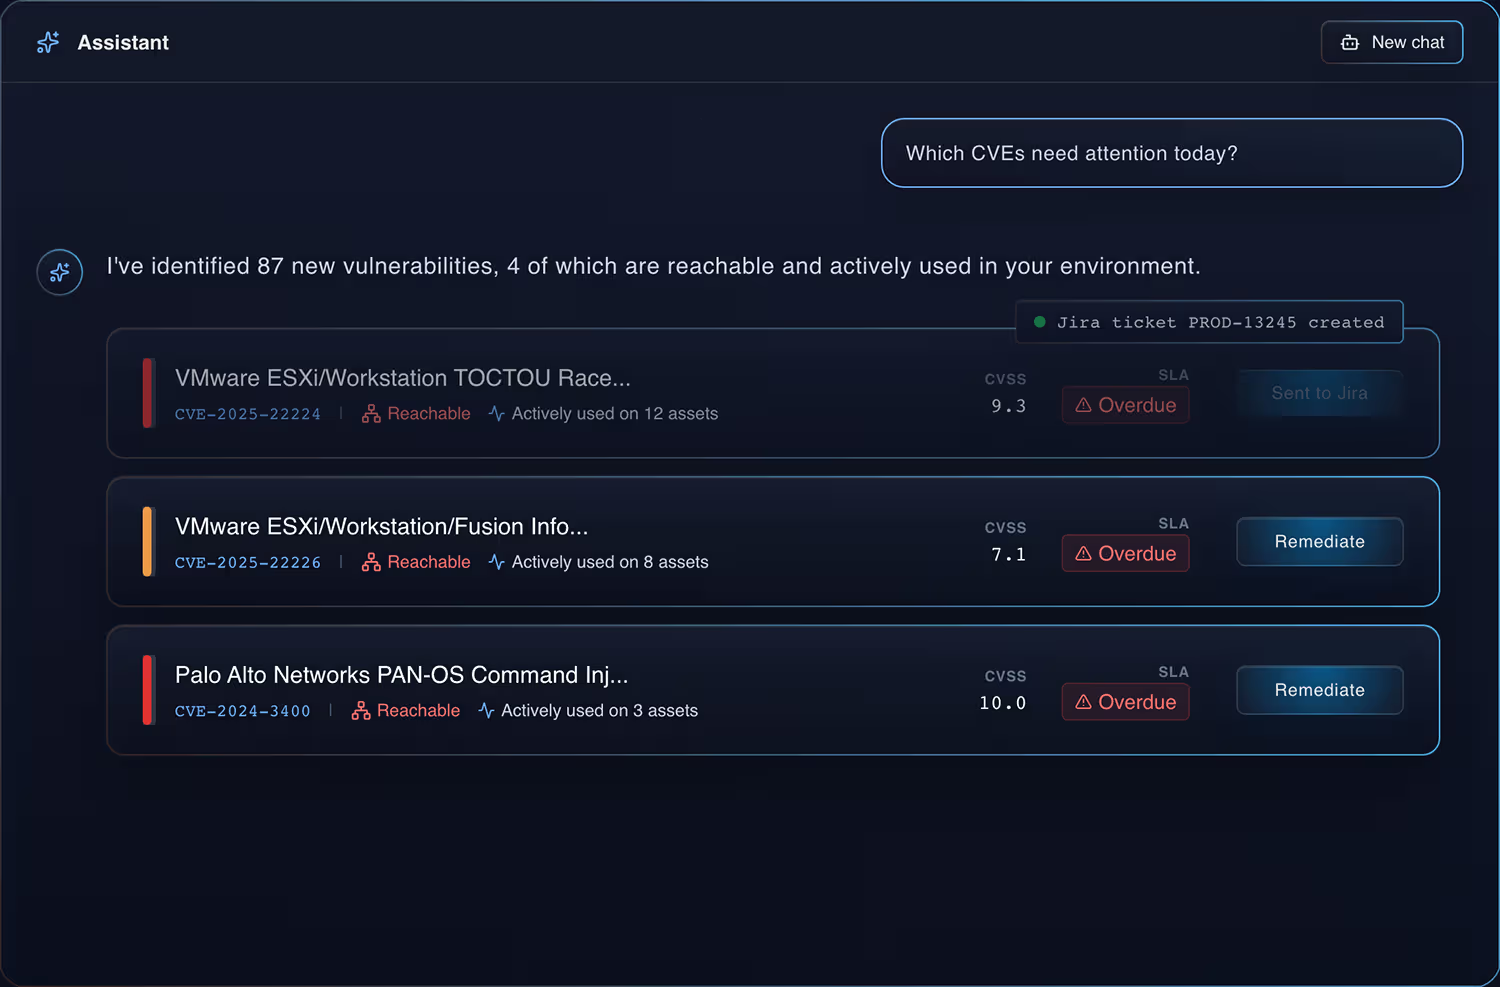
48,000+ CVEs published last year. Patch capacity can't keep up, and the gap widens every year.
The acceleration problem
AI accelerates both vulnerability discovery and exploitation. The window between disclosure and attack shrinks by the month.
The coverage problem
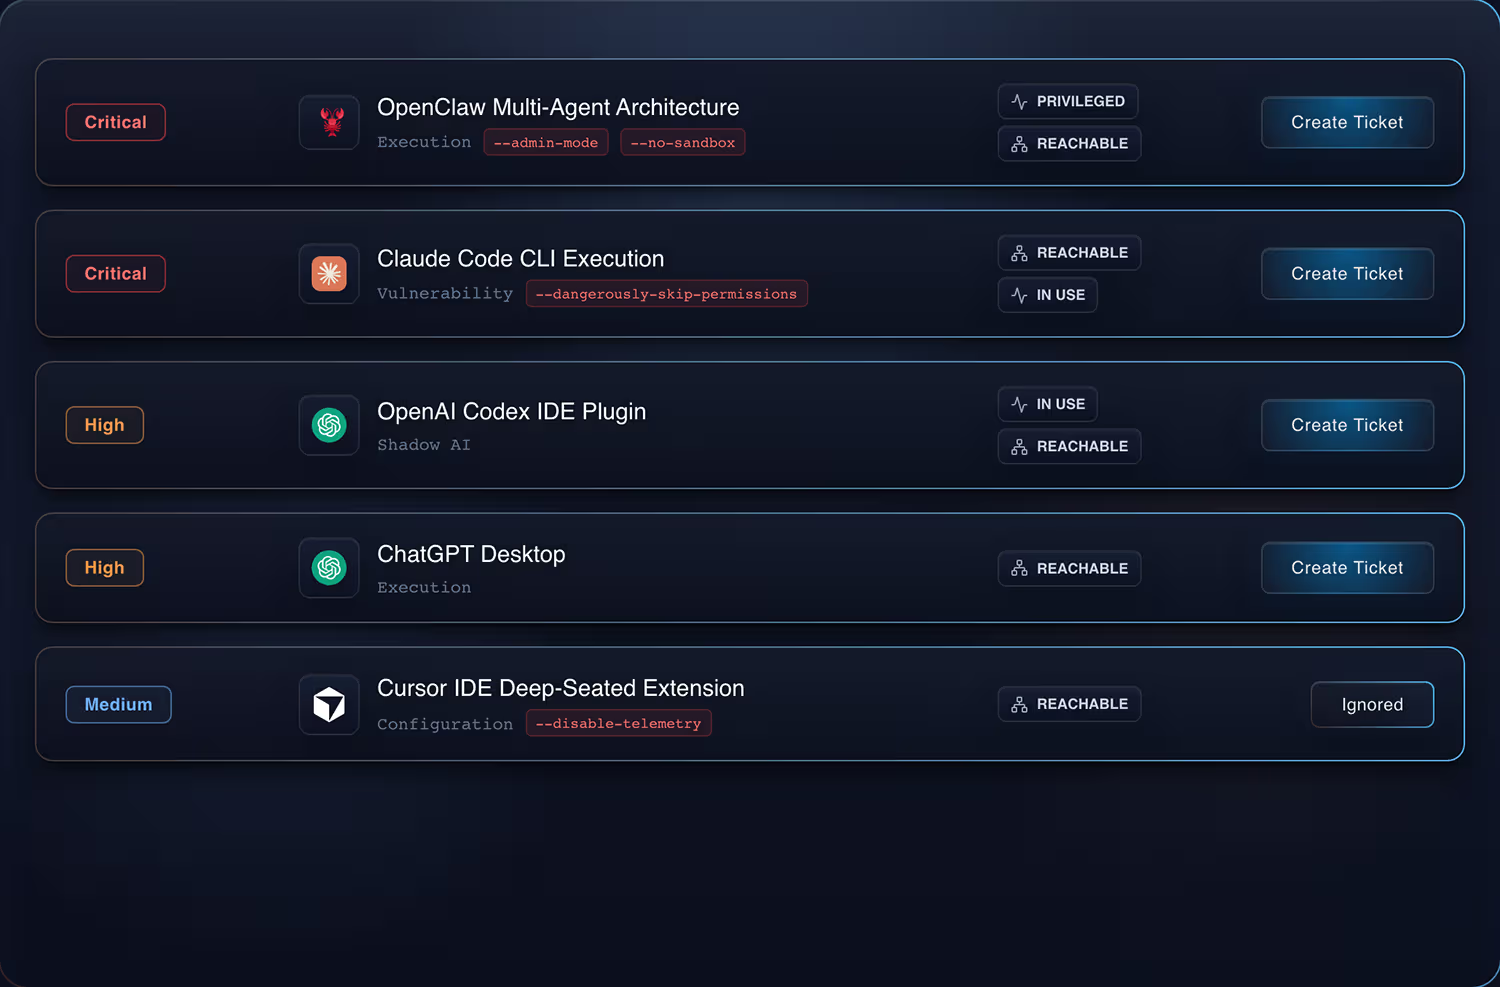
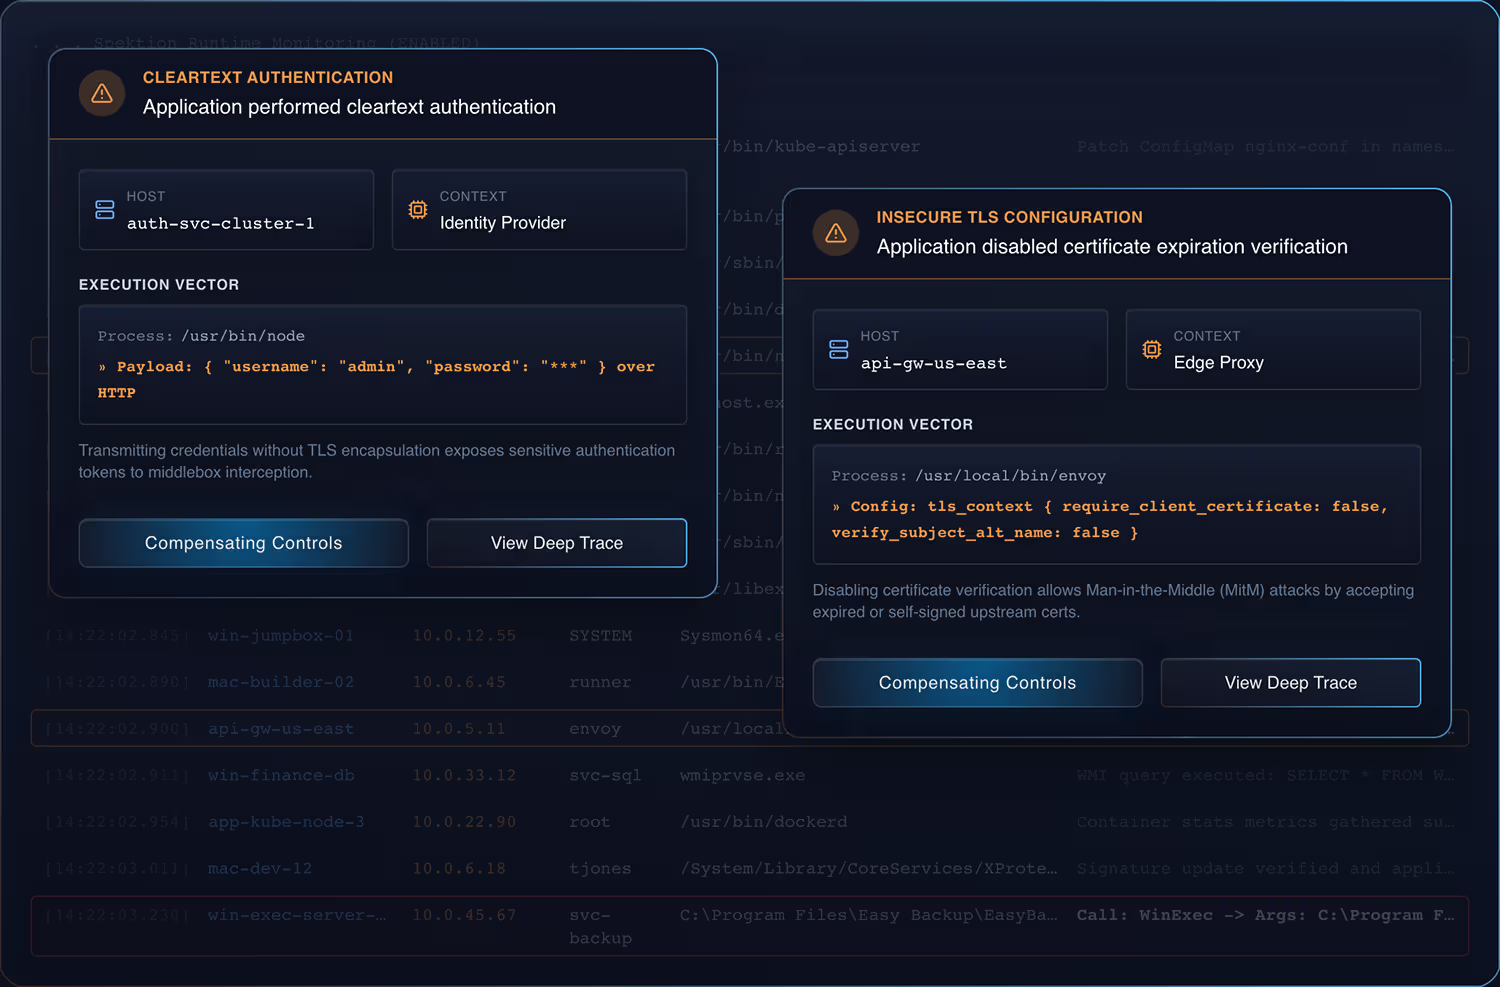
Zero-days, custom applications, and internal tools will never have a CVE. Scanner-only programs are structurally blind to them.
We lived these frustrations as security leaders.
Then we built Spektion to solve them.
Act on what's exploitable.
Not just what's vulnerable.
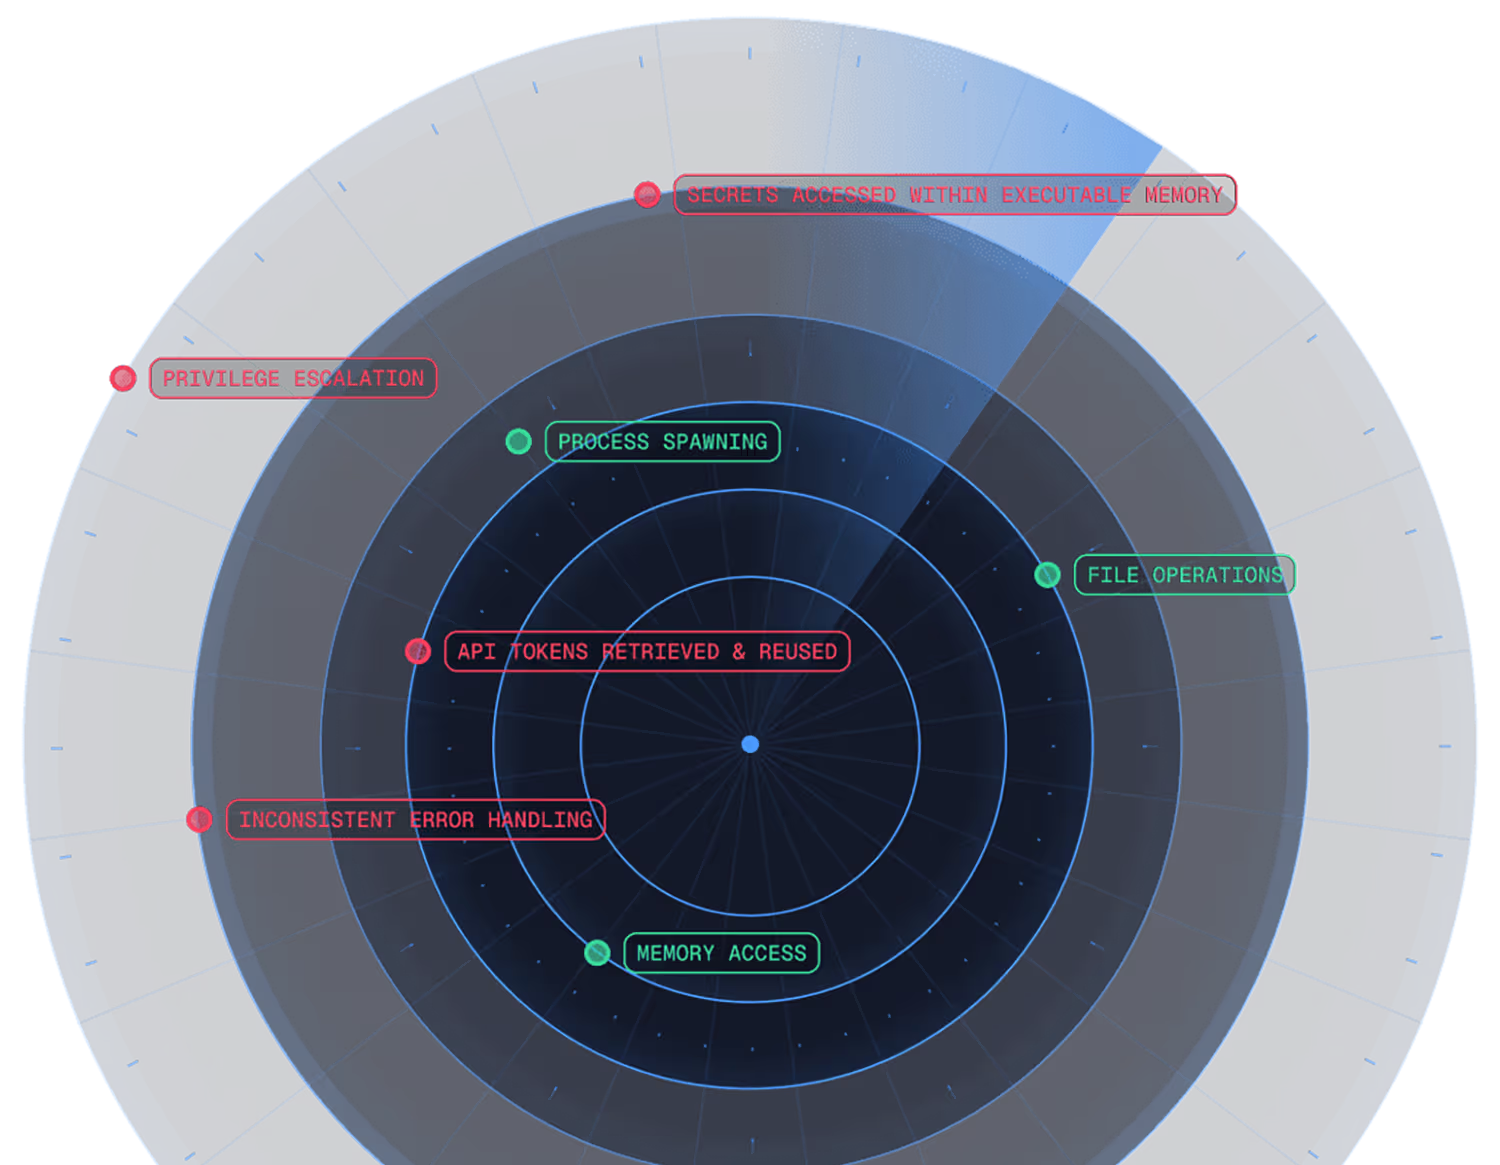
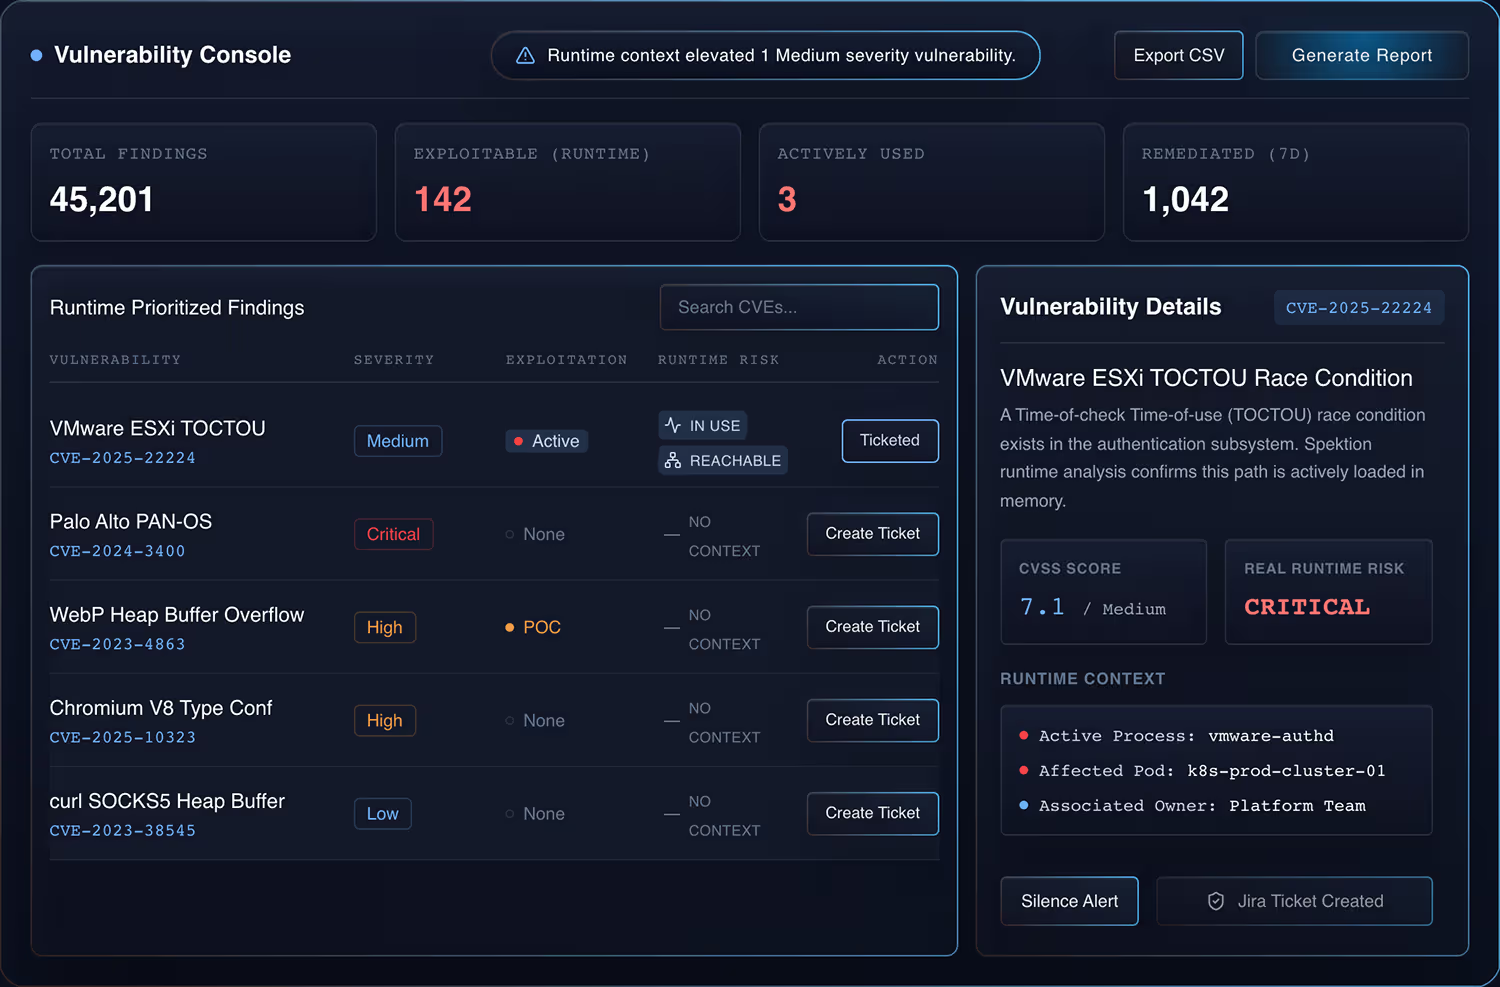
Is the software running? What privileges does it have? Is it network-exposed? What can it reach if it is compromised? Spektion answers the questions vulnerability scanners can't so you know what's actually exploitable in your environment and can act on it.
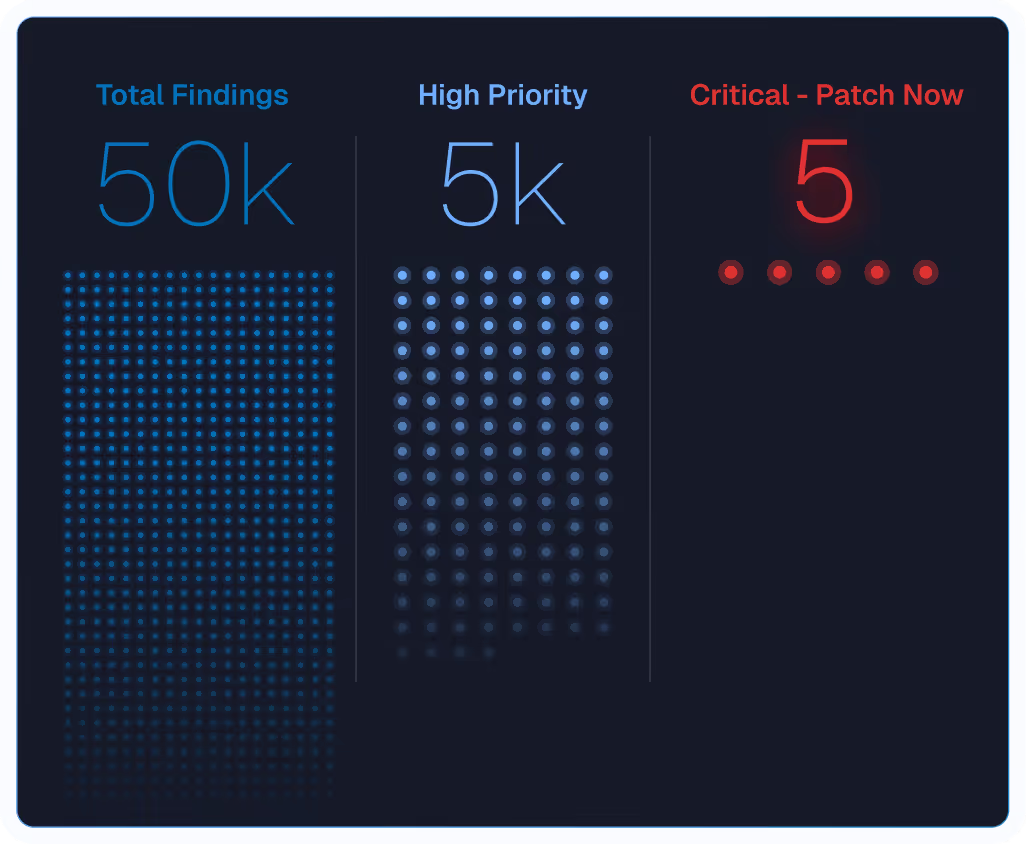

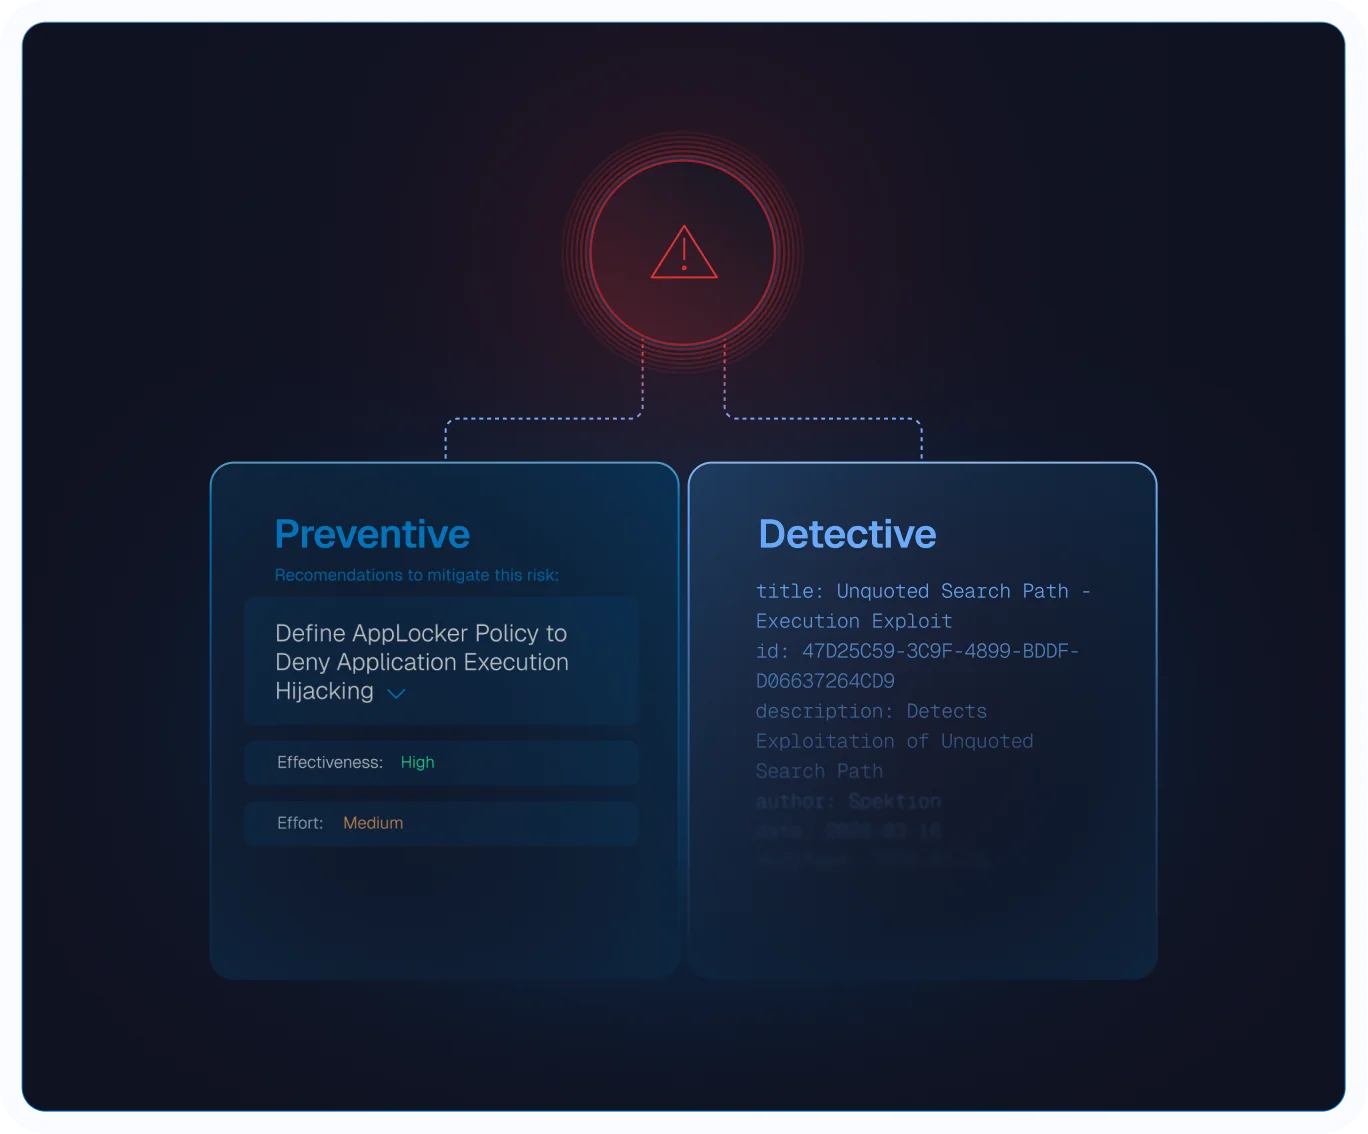

This is what risk reduction looks like.
Here's what organizations achieve with Spektion.

Critical backlog reduction in just one month.
Attack surface reduction by removing unused software.
Less manual work from DIY prioritization methods.
Trusted by security leaders.
Here's what some of our customers have to say.